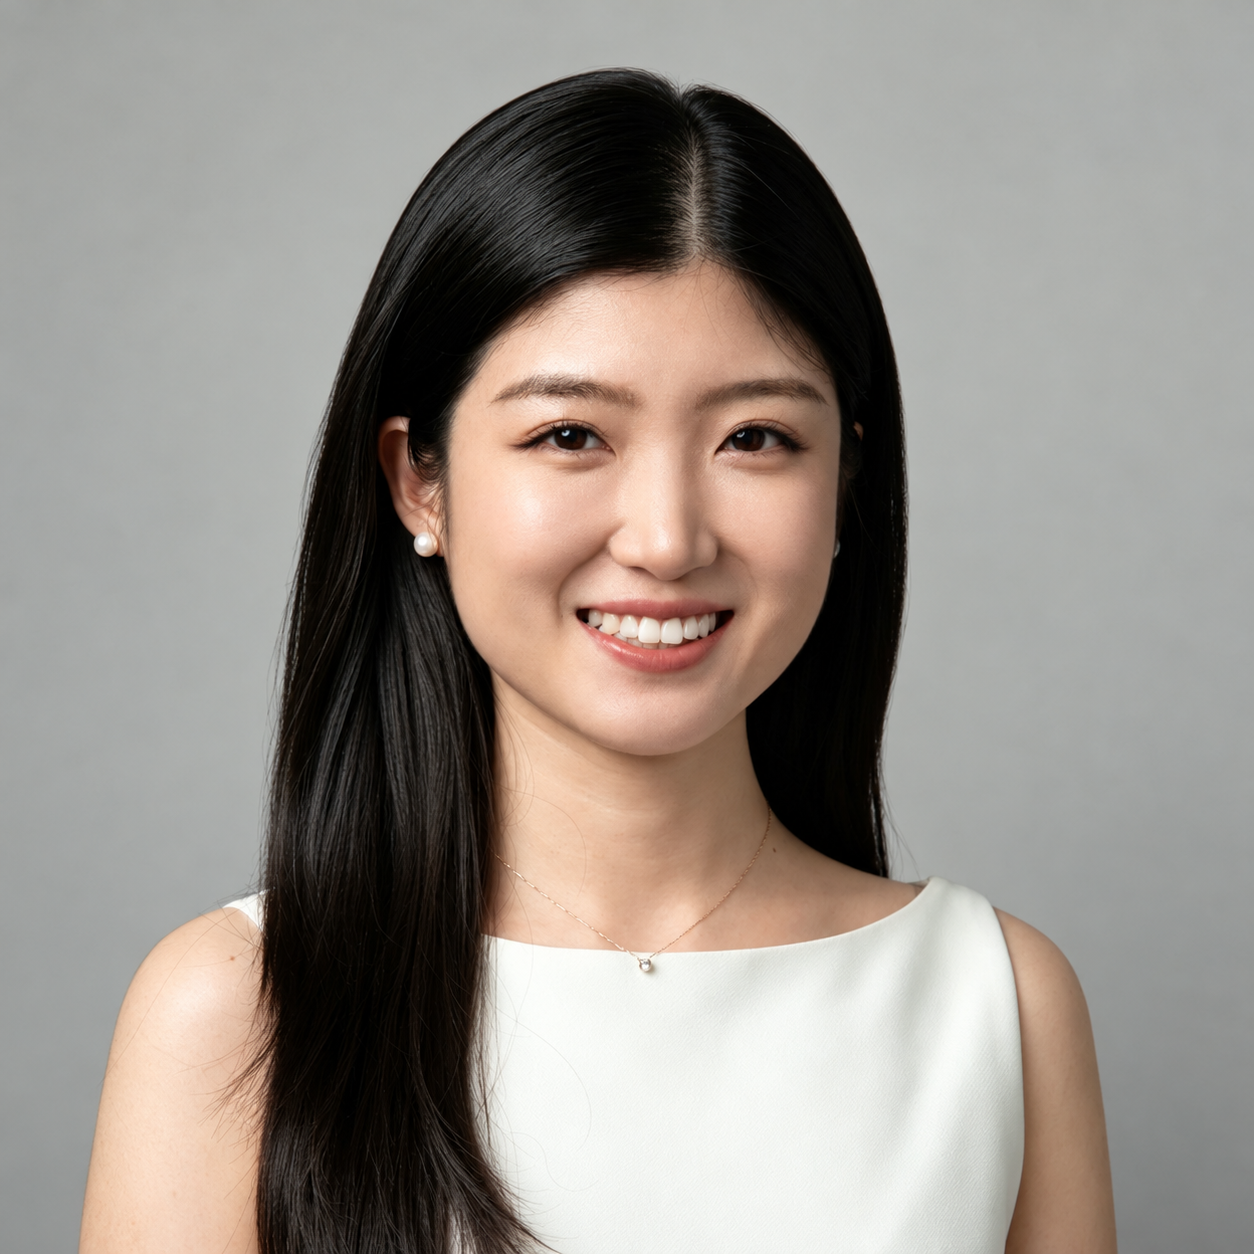
About Me
I’m Zirui Gong, a PhD candidate in Computer Science at Griffith University and a member of the RISE Lab and TrustAGI Lab, supervised by Associate Professor Leo Zhang, Prof. Shirui Pan, and Dr. Yanjun Zhang. My research focuses on the security and privacy of machine-learning systems, including federated-learning security, privacy attacks, differential privacy, and privacy and safety for large language models.
I am also currently a Research Assistant and member of the ASTAPLE Lab at The Hong Kong Polytechnic University, working with Associate Professor Qingqing Ye on differential privacy, privacy attacks, and privacy-preserving techniques for collaborative LLM inference systems.
Publications
- Zirui Gong, et al. “ARES: Scalable and Practical Gradient Inversion Attack in Federated Learning through Activation Recovery”, in IEEE Symposium on Security and Privacy 2026 (S&P).
- Chen, Z., Zirui Gong, et al. “Beyond Denial-of-Service: The Puppeteer’s Attack for Fine-Grained Control in Ranking-Based Federated Learning”, in Proceedings of the Web Conference 2026 (WWW 2026).
- Zirui Gong, et al. “Not All Edges are Equally Robust: Evaluating the Robustness of Ranking-Based Federated Learning”, in IEEE Symposium on Security and Privacy 2025 (S&P).
- Zirui Gong, et al. “Agramplifier: Defending Federated Learning Against Poisoning Attacks Through Local Update Amplification”, IEEE Transactions on Information Forensics and Security (TIFS), vol. 19, 2023, pp. 1241–1250.
- Li, Yuqi*, Zirui Gong*, et al. “Production Evaluation of Citrus Fruits Based on the YOLOv5 Compressed by Knowledge Distillation”, in International Conference on Computer Supported Cooperative Work in Design (CSCWD).
Teaching
At Griffith University, I work as a Teaching Assistant for courses such as Trustworthy AI, Deep Learning, Ethical Hacking, Application Systems, and Programming Principles. Additionally, I contribute as a Course Content Designer for Security Operations Centres & AI, helping students build both theoretical and practical expertise.
Research Interests
- Machine-Learning Security and Privacy
- Federated-Learning Security
- Large-Language-Model Privacy and Safety
- Differential Privacy
- Privacy and Gradient-Inversion Attacks
- Adversarial and Trustworthy AI
Contact
- 📧 Email: zirui.gong@griffithuni.edu.au
- 📍 Location: Gold Coast, QLD, Australia
- 🔗 Google Scholar